Who maintains education AI, the backbone of software infrastructure, and a new open source document tool.
Home Blog
#237 – Robert Abela on WordPress Security and the Battle Against AI Threats
Transcript
[00:00:19] Nathan Wrigley: Welcome to the Jukebox Podcast from WP Tavern. My name is Nathan Wrigley.
Jukebox is a podcast which is dedicated to all things WordPress. The people, the events, the plugins, the blocks, the themes, and in this case, the state of WordPress security in 2026, and the battle against AI threats.
If you’d like to subscribe to the podcast, you can do that by searching for WP Tavern in your podcast player of choice, or by going to wptavern.com/feed/podcast, and you can copy that URL into most podcast players.
If you have a topic that you’d like us to feature on the podcast, I’m keen to hear from you, and hopefully get you, or your idea, featured on the show. Head to wptavern.com/contact/jukebox and use the form there.
So on the podcast today we have Robert Abela.
Robert has been working in IT security for 25 years, ranging from antivirus software to web security scanners, and for the past decade has been running Melapress. A company focused on WordPress security plugins, particularly around user visibility, authentication, activity logs, and 2FA.
Robert is here to talk about the 2026 WordPress security survey. This is an annual project now in its fourth, or fifth, year gathering data from a wide range of WordPress professionals across agencies, enterprise teams, freelancers, and product owners. The conversation today is focused on the biggest security challenges and trends facing WordPress users in 2026.
We start off with some sobering stats. Over 67% of survey respondents reported experiencing at least one security incident in the past year, and concerns about WordPress security remain high, especially among less technical users.
We chat about the disconnect between awareness of security threats and actually taking steps to mitigate them, such as breach recovery plans and team training.
The discussion also explored the different types of risks that worry site owners. Site downtime, defacement, reputational damage, data loss, and even legal compliance issues. How the shakeout depends on the type of site, whether it’s e-commerce membership, a news outlet, or a simple brochure site.
We also talk about the tendency for even experienced WordPress users to take a reactive approach, only addressing vulnerabilities after something has gone wrong.
Towards the end of the episode, we discuss the rising impact of a AI on security, the explosion of AI facilitated vulnerabilities, and the shifting landscape of risk and response. There’s a healthy dose of reality, some optimism about the tools and best practises available, and plenty of good advice, especially for smaller teams and freelancers who may not have access to enterprise level resources.
If you care about keeping your WordPress sites secure, or want to understand where the community’s biggest concerns and opportunities are in 2026, this episode is for you.
If you’re interested in finding out more, you can find all of the links in the show notes by heading to wptavern.com/podcast where you’ll find all the other episodes as well.
And so without further delay, I bring you Robert Abela.
I am joined on the podcast by Robert Abela. Hello, Robert.
[00:03:48] Robert Abela: Hello Nathan. Thanks for having me.
[00:03:50] Nathan Wrigley: You’re very welcome. Nice to have you with us.
We’re going to chat today about internet security, but we’re going to be looking back over the past year, so the year 2026. Robert, can tell us a little bit about the company he founded, works for, and so on. It’s called Melapress, you can find out about that in just a moment.
But I would like to draw your attention to something which is going to really be the fulcrum of what we talk about. It is their 2026 WordPress Security Survey. Now, the easiest way to get that is probably to go to wptavern.com, search for the episode with Robert in it, and I will make sure it is linked in the show notes there.
But it might be a good idea to read it, because in about 10 minutes, you’re going to be able to capture absolutely everything that we’re talking about today, and you’ll get all of the data and, what have you. But that’s going to be the point of this episode, summarizing what happened in the security space in WordPress in 2026.
Robert, I guess there are a few areas in the WordPress space where it’s pretty important to know that we know, that you know, what you’re talking about when it comes to security, because we don’t want to have a lot of hot air from somebody who’s not experienced. So it’s an opportunity for you really to give us your bio and tell us a little bit about what you’ve been doing in the WordPress space, particularly around security, the companies you’ve worked for, the things that you’ve founded and so on. So over to you, Robert.
[00:05:07] Robert Abela: Thanks. I’ve been working in IT security for twenty-five years. I’ve always worked for software companies, software startups which worked in security industry. We used to do antivirus software, web security scanners, et cetera. I’ve had different positions. I started as systems engineer, QA, product management, project management, almost any field.
Anyway, and the last ten years I founded Melapress, and it’s a WordPress plugin business, and basically we develop a number of security plugins for WordPress. The security we do, we don’t do the typical firewall malware, et cetera, like the other, brands. We mostly focus on user visibility and authentication. So basically we have an activity logs plugin, and we also have a plugin for 2FA, passkeys et cetera. So we are focusing much more, on what happens post login once someone logs into WordPress, rather than the whole hardening and protection.
[00:05:56] Nathan Wrigley: Thank you for that. So anybody that’s interested, anything that we mention today, including the URLs of the companies that Robert has just mentioned, so Melapress, you’ll be able to find those in the show notes as well.
So the 2026 WordPress Security Survey, how many times have you actually run this? So obviously we’re looking at the 2026 version. Have you done this a couple of times and refined the way that you’ve done it and the way that you’ve surveyed over many years?
[00:06:21] Robert Abela: Yes. I’m not sure if this is the fourth or fifth year. But yes, we do every year, we’ve had more respondents. This year, by the way, it was the highest ever with 219 respondents. We had more, but before we publish all the results, we go through the sheet. Maybe there are some duplicates. Maybe some of them are not correctly filled in, et cetera.
But yeah, we’ve been doing it for around four years, and we’ve also fine-tuned from where we gather the data. For example, the first year, we’re only sending our newsletter basically, but this year we’ve done a lot. We’ve promoted the survey through third parties. We’ve gathered responses from WordCamp Europe, in person, through a number of other conferences, et cetera.
So while there is still a percentage that most probably are our users or our clients, still the biggest percentages is spread out to a wide range of different type of WordPress users, ranging from people who work for agencies, developers, designers, but also people who work with WordPress in bigger enterprises or businesses.
[00:07:15] Nathan Wrigley: Okay, so yeah, caveat emptor. With that in mind, the limitations, or otherwise, of the numbers that you’ve got represents what you’ve got in this survey.
And essentially, what it boils down to is a, it was kind of a bunch of questions which then led to a bunch of information being spat out the other side. And I’ve summarized it into about 10 bullet points. It may very well be that I’ve missed a few bits and pieces, but be interesting to go through, and you can lend your experience as to whether or not there’s been any change, whether things have got worse, whether things seemingly have got better.
We’ll begin, if it’s okay with you, with the top item, which I suppose, came out, which was a concern around WordPress’s security, or the things that can happen around WordPress and security. And what came out of it was that 7.85 out of 10, so 78 and a half percent, I suppose you could describe it as. They were developers who were expressing basically that they were concerned.
Now, I don’t know if you have more telemetry, like what concerned means, but off the face of it, that seems like quite a high number. If the platform that you’re using to build websites, you are in the sort of mid-70s concerned, is there anything you wanted to add to that or is that just the sort of top level statistic?
[00:08:28] Robert Abela: No. That was like a top-level statistic, a question we ask, like if people are concerned or they have worries about their WordPress, the security of their website.
What’s funny is the last few years, the level of concern has been the same. However, also we’ve noticed that people who have some sort of recovery plan, et cetera, also remains the same. So the level of concern has remained the same. So the majority of people know that something can happen to their WordPress website, especially now with AI, et cetera. It’s even more, things are moving much faster.
However, it seems like people are not taking the next step, as in like taking action to make sure nothing happens. What I’ve noticed as well, once we break down those who have concerns and what job they have, if they’re developers, or with their security people, et cetera. There’s this correlation, like, the more informed someone is, the more is involved in the tech aspect of the website, the more understanding they have on how things work, the less concerned they are.
So maybe it could also be education or awareness because of course, if you don’t know about how something works, then of course you are much more concerned. How you’re going to protect it? However, if you are, let’s say, a developer and has an understanding of sessions, cookies, the usual things, like passwords, maybe you’re a bit less concerned because you feel you are a bit more in control of how you can protect your website and what you can do.
[00:09:39] Nathan Wrigley: It seems like on the face of it, I should say, it seems like 78%. It seems like quite a lot.
[00:09:44] Robert Abela: Yes.
[00:09:45] Nathan Wrigley: If I had any kind of intuition, let’s say I was to go out into my car and drive around the street, if I thought that 78% of the time there was going to be some potential accident. Or I was worrying of the time about the possibility of an accident, I don’t think I’d be getting in the car. So it’s kinda curious. But, let’s move on.
So the next data point that dropped out was 67.7%, so let’s call it 68% of respondents. Now this is fairly shocking, and maybe this number will actually start driving up in the years to come, and we can get into that later.
68% of respondents had experienced at least one known security incident, with many multiple incidents. Now, that really is shocking to me. Closing in on 70% of people have had some kind of incident. I don’t know what, or maybe you do, what the magnitude of that is, but did that surprise you? Did that seem like a really large number?
[00:10:38] Robert Abela: 67.7 of all respondents, correct, they reported one security incident. I’m not surprised because almost everyone I speak to at WordCamps, even non-WordCamps, other events, someone down the line has had some security issue. Not just with WordPress, but especially with WordPress. And the funny thing, it’s not even funny, but 13.2% of those are repeat targets, which means they have experienced more than five security incidents.
Now, why does it happen? There are a number of reasons. Outdated software, lack of user awareness. In fact, what’s really more concerning is, I have some numbers here actually I can tell you. Yes, we’re still looking at some other statistics. Only 27.9% reported like they have some sort of training for their users. And only 37% use logs. At least 2FA’s a bit higher, it’s around the 40% something. I don’t have the exact number right now.
So yeah, so I’m not surprised because there is still a lot that can be done from website owners, from agencies, from everyone, to make sure we take down that number, and not everyone. Or so not the majority of people experience some sort of security incident on their website.
[00:11:41] Nathan Wrigley: Yeah, it’s curious. It’s not really a conversation. When I’m at events or chatting to fellow WordPressers, security is not the default conversation that I have, because I’m not a security person. So I end up chatting about, I don’t know, custom post types and how to do various things that I’m doing. Maybe podcasting in the WordPress space or something along those lines.
You, I guess, are having these conversations, and it’s very much in the territory. It’s in your wheelhouse. And so maybe it’s not a surprise to you that 67-plus percent of people have had something in the last year. But, on the face of it, that just seemed like so many. If I see 1,000 people at a WordCamp and I think, “Well, 670 of those have had a problem during the course of this year,” gosh that really does seem like a systemic problem.
And I know that outside of the WordPress community, WordPress gets a bit of a hard rap, on the security front. It’s insecure and what have you, and, all of the caveats. We know that really isn’t typically the case for WordPress Core. Tends to be the addition of code and plugins and themes that adds that on top. But I’m still surprised, feels almost like if the mainstream press got hold of your survey and just pull out that one statistic and bandy it around, it doesn’t feel great, if you know what I mean.
[00:12:53] Robert Abela: Yes. I think WordPress gets a lot of bad rep also because it’s very popular. As in like pre-WordPress, I’ve used web servers before as in like custom PHP websites, .NET, IIS, Apache, et cetera. Websites used to get hacked as well in the thousands. The thing is that you couldn’t point your finger to one type of website, you know because they were all custom. So these problems have been happening since we started having websites, quite frankly.
With WordPress, unfortunately it happens and we have a bad rep because I think there are two things. Look, first of all, it’s very popular, so it’s always there. If WordPress power is around 42, 43% of the, or maybe it went a bit down, but anyway, let’s say 40%.
[00:13:30] Nathan Wrigley: Roughly, yeah.
[00:13:32] Robert Abela: Yeah, The chances, for every 10 websites, four of them are going to be WordPress. That’s a common denominator. So of course, WordPress is going to get a lot of attention.
I also think, again, goes hand in hand with how many people have security concerns. WordPress has made it very easy to launch your own website, which is a good thing. However, of course, those same people who launch their own website, maybe they don’t have the technical understanding and experience what it takes. Because setting up a website’s one thing, but keeping, managing a website for a year, two, three, and growing it, adding new functionality is another thing. So most people might not have the experience that they have, so of course, it’s much easier to find security issues with these type of websites.
[00:14:10] Nathan Wrigley: Okay, we’ll move on anyway. So we’ll talk about the concerns. So you’ve obviously polled your recipients of the survey about the kind of things that they were worried about. So what are the outcomes that they fear the most, if you like?
And website availability, so the taking down of a website came in at number one, with 55.8. And then in no particular order, but these are the two that I picked out. The fear of being defaced, so the website in some way being amended, or there being some reputational damage because of what the amendment was. I don’t know, maybe there was some imagery, or some slightly political content that ended up on your website.
That was just slightly south of the availability, so that was 54.2%. And then dropping a full 10%, so 46.4%, was the worry about data theft or loss. Frankly, I’m not surprised by that. I guess any developer’s nightmare is their website actually disappearing off the internet. That’s number one, so that doesn’t surprise me.
I remember in the day, 15 years ago, defacement was the thing. Honestly, I can’t say that I’ve been browsing the internet recently and seen something that’s been defaced. It seems like the hackers have all moved on. Maybe there’s things buried in the source code that I don’t know about.
Yeah, it doesn’t surprise me that the availability is the main thing. But I am surprised that data loss comes in third, if you like. I personally would have had that as number one, especially, if you’ve got a, I don’t know, an LMS, or you’re connecting with a CRM, or you’ve got form data which potentially is capturing something personal that the GDPR would worry about. So there’s no question, just if you want to comment on those particular things, go for it.
[00:15:42] Robert Abela: No, definitely. Those are the numbers based on all the respondents. But if you start breaking down the numbers, there’s more nuance to, to these things. So for example, if you look, those who are concerned about website availability, or defacement, are usually those who have content websites. Mostly based on content, news, magazines, et cetera. Those who are more concerned about financial loss or data theft are more the e-commerce websites.
[00:16:08] Nathan Wrigley: Oh that makes sense. Yeah.
[00:16:09] Robert Abela: The membership websites, et cetera. In fact, the membership websites are as well more concerned, for example, about compliance because of privacy. So those numbers, like fifty-five point eight percent, those are from the all respondents. But as soon as you break all that down, it differs a bit on the type of website you have.
And it’s expected because if you have an e-commerce website, of course you are dealing with billing details, payments, and all this stuff. If you have a membership website, maybe you are also dealing with payment details, but you are also dealing with much more data. Maybe you have some sort of internal chat. People are sharing their addresses on it, their personal information. So that you are more concerned about GDPR or any sort of compliance, et cetera.
But if your main selling point is if you have a content website, a news website, and your main selling point is your website being available, then of course that is your biggest worry.
[00:16:53] Nathan Wrigley: That’s an interesting split of the data there. That makes perfect sense, of course, now that you say it in that way it really is obvious.
So that was you polling your respondants respondents there, and you were trying to figure out what their worries were and what they were into and all of that kind of stuff.
And then we sort of to move to a different realm where despite all of that being said, so, you know, got a lot of people worried. We’ve outlined some of the different worries that they have, depending on the type of website that they’ve got.
From all of that, if you’d have ended the survey there, I would have assumed at that point that everybody had something in the back pocket to pull out, an SOP or something like that, to pull out in the event of an actual problem. If data theft is apparent, we do this. If the website goes down, we do this. But your survey reveals entirely the opposite.
So the high numbers on the one side, the fear numbers, are not mirrored by the what we’re going to do about it numbers, because you go straight into the high 20s, so 27.9% had a breach recovery plan. So how to get back from a problem with your website being, let’s say, hacked, let’s use that word. And 26% provided some sort of training for their team, some sort of security team training, that kind of thing.
Again, does that surprise you? You’re in this space. Maybe that’s really typical, but given the high levels of concern, there seems to be a real disconnect with what we’re going to do about it. That’s curious.
[00:18:18] Robert Abela: I’m not surprised, in the sense, it’s very common. The majority of people, especially nowadays, there’s much more knowledge that, yes, websites can be hacked, this can happen. However, that doesn’t translate. People don’t have the, I don’t know if it’s the resources, the means, the time to actually take action on it, to prepare some things. So, I’m not surprised.
Again, similar to what we discussed before, there’s a bit more nuance to these type of numbers because you said only 27.9% has a breach recovery plan. Actually, that’s based on all the respondents, but typically the number is much less, because when you look at it, from the respondents, from all those who have a security breach, from those 27.2%, 70.2% which have control in place are corporate or brand websites, which means they have their own in-house team. Only those, 70% of those have their own, have their activity logs, have their firewalls in place, have a recovery plan in place, et cetera.
So the number of, let’s say, the non-branded, the smaller websites, yeah, they have absolutely nothing. They have no sort of recovery plan or anything like that. In fact, the numbers are much smaller. Only 23% of those websites typically have some sort of recovery plan.
[00:19:23] Nathan Wrigley: Okay.
[00:19:24] Robert Abela: I’m not surprised because usually, especially if you’re an enterprise, or a bigger business, you are bound by more compliance. Maybe you have more security people on board who are much more aware what can happen of what they need to do. But yeah, the average website doesn’t have these things.
[00:19:38] Nathan Wrigley: Yeah. I wonder if your data here might be skewed by the type of correspondent that you got. So for example, who knows how many blue-chip companies, have submitted to your information gathering here. Perhaps not many, but maybe you got lots of WordPress community members, and so the data might be skewed in that direction. But that’s an interesting point. So dependent upon the nature of the website and the type of team they have behind it.
But it is still, regardless of all of that, it is still quite low. And I was using my analogy earlier about insurance, and I think that applies here. Insurance is the most uninteresting thing to purchase because you spend this money and, let’s say for example, you got home insurance. I would imagine most people typically go through a year and they never make use of it. Sorry to anybody listening who has obviously had to make use of that. But the moment you need it is the moment that you’re glad of every single penny that you’ve sunk into that, and I guess that applies here. If we can persuade people to get that data breach recovery plan, whatever it may be, have that in your back pocket, that would be a useful thing to have.
[00:20:38] Robert Abela: Yeah. As I’ve said in the beginning, I’ve been working in IT security companies, security software companies for 25 years. All of them, the most common sales opening, like sales reason, like people coming to us like, “Hey, this happened, so now I need this.” They’re always after they’ve been hacked, after they’ve been a leakage, after there’s been something wrong.
Very few proactively come and as I said, like the bigger enterprise companies, because they have certain regulations and stuff and certain budgets that they invest in these things. But the average website, yes, first they have to experience something, and then. I think it’s, in all fairness, I think it’s common human nature. It’s not just about IT. We tend to be all humans. We tend to be like, “Oh, we’ll see later,” and then if it happens, “Ooh, I should have…” it’s always like that.
[00:21:17] Nathan Wrigley: Well, there’s also that calculus of how much time does it take to recover. So for example, if you’ve got a brochure site, and you’ve got backups going back for many many months you can restore to a point that you’re fairly sure that everything was actually fine, and the breach has been mitigated by going backwards in time. But it’s just all the wasted time. It’s the wasted time going through the backups and seeing, okay, is this backup, does it have the malware in as well? Okay, that one does. What about this one? What about this one?
And there’s no knowing how long that’s going to be, and the minute you step, as you said, into e-commerce and you’ve got transactions happening every couple of minutes, and then you’ve got receipts and you’ve got to fulfill those orders, and somehow, oh boy, yeah.
[00:21:59] Robert Abela: Yes. Then it’s a different ballgame. Yeah.
[00:22:02] Nathan Wrigley: Different ballgame isn’t it? Yeah.
Okay, so the next point that we’re going to move on to is actually one that you probably just made. And it’s that the detection in most cases, well actually not most cases, in many cases. So 42.6% of your respondents said that their detection is mostly retroactive. So that is to say the thing has already gone wrong. Somebody in the 42.6% of the case is because they see something on the website. They’ve noticed that something isn’t quite right, something looks out of order.
38.4% because they were actually inspecting the logs. That tells me that whoever’s inspecting the logs is doing diligent work. That’s kind of interesting. So don’t know if you want to comment on that, but basically a lot of people are figuring this stuff out after the thing has happened, as you described, not before the thing has happened.
[00:22:51] Robert Abela: Yes. So there are four criteria. So 42.6%, as you said, is common website behavior, either detected by their team or by clients. 38.4 via logs. Now, the logs is a bit, it can be reactive and proactive, because with the logs, you can actually, in fact, we have some notes on this, but I don’t have the exact numbers right now. Because some of them were actually by someone analyzing the logs, but some of them were actually because someone has configured notifications based on the logs, like a sort of intrusion detection system.
And so if, I don’t know, if X login happens after X time, whatever, please send me an email or an SMS, and that, it’s still reactive in a way, but at least they could act right away as soon as it’s happening. Yeah.
[00:23:31] Nathan Wrigley: Yeah kind of proactive reactive, isn’t it? That’s a really interesting subcatagory.
[00:23:33] Robert Abela: Exactly, yeah.
[00:23:34] Nathan Wrigley: Yeah.
[00:23:34] Robert Abela: So yeah, but yeah, it’s still reactive because then you have 35.6% they knew through their web host, and 30% they knew through some sort of malware scanner alerts on their website, et cetera.
[00:23:45] Nathan Wrigley: Okay. Again, just kind of interesting data coming out.
So the next one, incidents most commonly resulted in downtime for the website. So that’s pushing up to 70%, 68.4% of whatever happened, resulted in some downtime. And then I don’t have the numbers for the following data, but I guess it decreases from here.
The next thing was reputational damage. That was a result of some sort of incident. And then search engine ranking is affected. That’s an interesting byproduct.
This one’s brutal. Client trust disappearing. That’s really interesting. And then in some cases, lost revenue. I imagine the lost revenue is being described as in some cases, because, as we described earlier, if you’re dealing with revenue, you’ve probably got more bulletproof security measures in place.
But the ones that sort of jump out to me there aren’t the downtime, because I would’ve assumed that. It’s really the curious byproducts of things like the reputational damage, the search engine damage. You can’t really get your hands on those, can you? There’s no real way of knowing what that’s going to look like or feel like, or how that’s going to affect your business this year or next year.
Just to know that, you wake up one morning to discover that you were in first place on Google after six years of hard SEO work, only to discover that you’re now in fourth and descending fast, that’s pretty brutal.
[00:25:01] Robert Abela: Yes. And in fact, if you break down those numbers a bit more, like 45.9%, there’s loss of search engine ranking, and that happens usually when search engines detect you have issues. I don’t know if you remember, Google used to have that page sometimes.
So that happens. When that happens, when the search engine themselves realise there’s an issue, you lose a lot of rank. The penalty you get there is very heavy. In fact, only 14.5 of those who have had some issues with the website has lost ranking because they have discovered their issues before the search engine did.
So again, that’s why you should be a bit more proactive because if your search engine finds out before you, the penalty, as you said, and you cannot really quantify it because God knows how long you will remain. As you said, if you were position one for six years in a row, now one fine day you’re on the second page, God knows how much work you need to go back up, and you cannot even calculate what the revenue loss is.
But when it comes to revenue loss, again, it’s the same. There are some websites, I’ve seen some websites where like they generate $70,000 per hour. So for every hour down, that’s $70,000 gone.
So yeah, there are lots, and of course, the reputation, on top of the reputation, there’s also compliance and legal consequences, especially in the US. Things are becoming much stricter now. If you had some issue, some customer data has been leaked, you have problems with the law, fines, and other similar stuff. So, the financial damage to all of this, of your website getting hacked, is very high.
Not just the reputation, losing customers, you might end up in court. You might lose your search engine ranking, and that is why most probably it’s a good idea to become a bit more proactive rather than reactive. Or it’s almost impossible to, there is no 100% secure solution, and that is why I think it’s very important to have good hardening, but also good monitoring, the whole process, the whole 360 degrees, the whole cycle.
[00:26:44] Nathan Wrigley: It’s such a curious industry that you’re in because, how to describe this? It would seem, or at least, it would be possible to perceive that this security survey is perfectly aligned with your business goals in a way. There’s loads of problems out there on the internet. There’s multitudes of ways that things can go wrong, and for every one of them, there’s, a WordPress solution out there.
But I know Robert. We’ve met many times before. I get the intuition that’s really not why you’re doing this, although somebody listening to this might have that sort of slightly, I don’t know, cynical approach that, Robert’s just saying this so that he can launch his Melapress products at you. Just put our minds to rest on that score. Why do you actually carry out this survey?
[00:27:25] Robert Abela: Good question. Actually, our plugins only address part of the security. There’s much more when it comes to firewalls, et cetera, that I still say hardening you still need. We don’t even cover it.
No, we do it, honestly, it started around four or five years ago, for me, it was just curiosity. It sounded like an interesting to do. Hey, let’s do a survey, just experimenting, et cetera. And we had very good response, and now we’re just, doing it honestly.
Like I really believe that by knowing, this is not just about WordPress security, about everything else. By knowing where other people are doing it wrong, you will learn from it. By knowing, okay, clearly I can see, for example, as we were saying, like seventy percent, seventy point two percent of enterprise and marked businesses usually have logs, usually have firewalls, et cetera. Maybe we should aspire more towards them and be more like the average website should have a bit more like things like that, and maybe they’re doing something right.
So yes, there is a lot to learn from surveys in general, not just this, any type of survey. There is usually a lot to learn. And that’s why we’re doing it as well, because from the first time we’ve done it, which started really as a curiosity project, we got so much good feedback. And actually the second year people were asking us if we are going to do it. Because yeah, people learn from these things.
I mean, of course there’s the benefit of it, hopefully it will promote as well a bit our plugins. But anyway, it’s going to promote all other type of security solutions. We are not, in fact, the survey is not tailored just for our plugin. It talks about everything. As I said, the whole security cycle. You have the hardening, you have the monitoring, updating, et cetera, and we only do one part of it, the monitoring aspect, basically.
[00:28:50] Nathan Wrigley: Before we move on to our sort of final bit, which I want to concentrate on AI, I’m just going to wrap up the security bit just by summarizing what comes towards the end. And it’s less about numbers, and it’s more about just conclusions that may have been drawn. But most of it, I think, would be fairly obvious from what we said. So I’ll just summarize it a little bit.
The first one is that e-commerce and membership sites tend to have greater security concerns and stronger practices. That kind of makes sense. I guess it reflects the nature of the business they’re in, and the kind of data that they’re holding, and the legal compliance that they may need to be concerend with.
In-house teams are more likely to have recovery plans. Again, I presume that’s fairly obvious. The boss, the head of the pyramid can sit down and say, “Okay, it’s your job now to crack on and do that. You’ve got a week to figure out all this sort of stuff,” and what have you. Whereas a freelancer sitting in their own office, there’s always regular work to be built, sites to be built and other things to do. So I can well imagine why that’s the case.
And sites, again, fairly obvious, sites with repeated security incidents tended to have stronger controls in place. Today, presumably, it’s a case of once bitten and all of that. Once you’ve actually had this nasty stuff happen to you, you’re pretty likely to make sure that does not happen again.
In summary, I suppose the reports really, the recommendations are focus on prevention, detection, and recovery rather than simply adding in more security tools, would be the way that I would describe it.
Okay, let’s move on then just before we finish. It is, as we’re recording this, it’s September 2026. In the more recent past, I want to say, I don’t know, the last two months, something like that, the WordPress security news bulletins have been on red alert really. We’ve had some charts being put out on social media which show the amount of vulnerabilities discovered, and also the amount of AI-based plugins that have gone into the repository. The supply chain attacks that have suddenly become a thing. A lot of it really because people can corral AI to do mischievous stuff and what have you.
I don’t really have a question, but I just wondered if you had a comment on where we are in September 2026, because it does feel as if there’s quite a lot of, there’s a lot of scope to be very doomer at the moment. It almost feels like the AI is winning the arms race, but maybe that’s not what you’re thinking from your end.
[00:31:04] Robert Abela: No, it looks a bit negative. I wouldn’t say AI is winning the race. Actually, people with malicious intent using AI are winning because AI is neutral in a way, like it depends on what people ask the AI to do.
[00:31:15] Nathan Wrigley: Yes.
[00:31:16] Robert Abela: But it is worrying, yes. The graph you are mentioning, I saw a graph shared by John Blackbourn, yeah, about the number of issues reported in the HackerOne WordPress vulnerability program, which is insane.
[00:31:28] Nathan Wrigley: Yes.
[00:31:29] Robert Abela: And they received more reports in the last week than they ever did in a whole number of months. So yes, it is worrying. You can look at it both ways. The same way attackers can use AI to find issues. We are doing it ourselves as well, quite frankly, because whenever there’s a new model out there from all of these vendors, most probably attackers are going to use them to scan our code, et cetera. So we’re doing it as well.
We always used to do the manual security analysis, et cetera, but now that we have AI, with every release, we just hammer the update and try to find as many issues as we can.
The reality is also that some, if not many of these vulnerabilities are not actually so easy to exploit. Like it’s really, the stars really have to align and it’s really, but still, it’s better safe than sorry. Because even though today it might be difficult to exploit a particular issue, in six months’ time, we might have technology that might make it very easy to exploit this type of issue.
It looks negative, but the same tools that attackers have, malicious users have, we have them as well. So it’s up to us to use them and be ahead of the curve, and use them proactively ourselves and before every update, during the whole development cycle. We should use them more often to make sure at least that we cover what other people can find before us.
[00:32:35] Nathan Wrigley: Yeah. I suppose the bit that I find curious is the optics of it. So, there was always this universe in which people would be able to throw dirt at WordPress because you know WordPress isn’t secure, and we talked about that earlier. It’s usually plugins and very rarely Core. Plugins, themes, additional code, what have you.
However, given that it would appear that people can stack 14 overlapping problems and create this one vulnerability from things that probably humans would never have conceived in the past. That then just lends into this narrative of, well there’s this deluge, this tidal wave of things that are coming at WordPress.
So I woke up this morning to discover in my feed BleepingComputer. I don’t know if you’ve seen this one yet today, but BleepingComputer have got an article with a CSV attached to it about yet another WordPress thing. And it just feels like that sort of day in, day out, there’s just another and another, and it’s that narrative that, that concerns me. It’s just that it gets away from us, that there’s one this day, there’s one this day, one this day, one this day.
And having to explain, “Look, calm down. That one was nothing. Okay, calm down. That one was also nothing. Okay, yeah, that one was something, but that one was nothing, that…” It’s just that constant fighting the narrative in an era where every day something seems to be out in the press, a problem that WordPress. Do you capture what I’m saying there?
[00:33:57] Robert Abela: Yes, no, and no wonder we get negative rep in the rest of the IT industry because, yes, we do get these news, and the numbers are very big. If you find a vulnerability in a plugin that has half a million installations, all of a sudden you see the news, “Oh, half a million WordPress websites are vulnerable to X.”
Unfortunately, yes. The thing is, WordPress in general, it’s very secure like. There are so many I’ve seen in my life, I don’t know how many custom web applications I have seen that are horrible in terms of security, like really horrible. It’s just because, of course, no one is seeing these because this might be a website in millions of websites, so no one is targeting. But WordPress, because it’s a popular platform, is going to be targeted.
But yeah, because the numbers are big, yeah, unfortunately, we do have a bad rep. And yeah, the news like to sensationalize things as well. So yeah, the rep is not good, no. But the reality is that it’s going to happen. It’s going to happen more often, most probably. It happened to us. All the vendors I’ve spoken to at WordCamp US and WordCamp Europe, they’re all the same. If you look at our plugins as well, maybe we used to get, I don’t know, maybe on average a vulnerability or two reported a year.
As soon as this whole AI started thing, all of a sudden within a month or two, you get like four, five, six reports like, “Whoa, what happened?” In just one week. It’s just reality. It’s up to us, as I say, we have to be more proactive. Of course, it’s easier said than done, but we have to be more proactive and try to use the same tools that attackers are using to make sure at least we detect them, yeah.
[00:35:13] Nathan Wrigley: Yeah, the bit that genuinely I find curious is what will be the calculus in terms of time that people can spend on this stuff. So as an example, if let’s say that by January 2027, many of us are having to spend a good proportion of every day, and by a good proportion, I don’t know, let’s say 30 minutes or something, browsing through the news to see if anything has cropped up. Or indeed to read the things that we know has cropped up because the fire hose of security news has gone through the roof.
This seems like it could happen, that we’ll all have to be mindful of it. And it’s just that sort of attritional wear and tear that, “Okay, really? Do I have to do this each and every day?” That will be interesting.
I suppose the flip side of that, curiously, is that it, how to describe this? It doesn’t do your business any harm because the more that people are concerned about their WordPress websites, the more security news there is, the more that they will be drawn to companies like yours. So it’s a very curious tightrope walk that you’re going to have to perform, I think as well.
[00:36:10] Robert Abela: Yes. Yes, it’s the reality. If I can do a shameless plug, at WordCamp US, I spoke about, WordPress user sessions and hijacking, and one of my lines was that all the things I had mentioned, but the talk is available on YouTube on the WordPress channel. All the things that I have mentioned, so many missed it, because if you look at user session hijacking, the bottom of it is all derives from user mistakes. A user making a mistake, that’s all it is.
And the reality is it all sounds dramatic. It all sounds like it’s the end of the world and apocalyptic. However, the reality is that, yes, nowadays, if you use a website, even as a user, you need to be aware of some basic things.
So yes, there are these news, and hopefully more and more people will become aware and more and more people need to become aware that yes, these are the dangers, these are like the risks of logging into a website nowadays. Of maintaining a website nowadays. It is. It’s like a double-edged sword. Like the news are making sometimes a bad rep for WordPress, but they’re also reaching more people that they need to wake up and say, “Oh, these are the risks, so we need to take action.”
[00:37:07] Nathan Wrigley: Yeah, it will be interesting in the face of AI vulnerability. It’d be interesting to see what the, let’s say hosting companies, let’s paint a target there. What they do to manage their stack, because obviously it’s going to be very important for them to make sure that the clients that they have. And how they position themselves in the news, and how they can portray the security solutions they’ve got. But as well as companies like you, you know, plugins and other firewall companies and things like that. Be interesting to see through 2027 how they manage that.
Okay. In which case we will wrap it up there. Just another quick reminder, go to the WP Tavern.com website, search for the episode with Robert Abela. You will be able to find the 2026 Melapress WordPress Security Survey over there. Download it, have a little bit of a look. And Robert, are you available anywhere online? Do you, other than Melapress’ do you actually make yourself available? And if so, where can we find you?
[00:37:58] Robert Abela: Yes, I’m active on LinkedIn, Robert Abela. I’m active on X.com, and I finally also have my own website. It’s more on personal things quite frankly, but yeah, it’s robertabela.me.
[00:38:08] Nathan Wrigley: In which case I will bury those in the bottom of the show notes as well.
[00:38:12] Robert Abela: Thanks.
[00:38:12] Nathan Wrigley: So that you can find those. Robert Abela, thank you for chatting to me today. I really appreciate it.
[00:38:16] Robert Abela: Thanks likewise.
On the podcast today we have Robert Abela.
Robert has been working in IT security for 25 years, ranging from antivirus software to web security scanners, and for the past decade has been running Melapress, a company focused on WordPress security plugins, particularly around user visibility, authentication, activity logs, and 2FA.
Robert is here to talk about the 2026 WordPress Security Survey, this is an annual project, now in its fourth or fifth year, gathering data from a wide range of WordPress professionals across agencies, enterprise teams, freelancers, and product owners. The conversation today is focused on the biggest security challenges and trends facing WordPress users in 2026.
We start off with some sobering stats, over 67% of survey respondents reported experiencing at least one security incident in the past year, and concerns about WordPress security remain high, especially among less technical users. We chat about the disconnect between awareness of security threats and actually taking steps to mitigate them, such as breach recovery plans and team training.
The discussion also explored the different types of risks that worry site owners, site downtime, defacement, reputational damage, data loss, and even legal compliance issues, how these shake out depends on the type of site, whether it’s e-commerce, membership, a news outlet, or a simple brochure site.
We also talk about the tendency for even experienced WordPress users to take a reactive approach, only addressing vulnerabilities after something has gone wrong.
Towards the end of the episode, we discuss the rising impact of AI on security, the explosion of AI-facilitated vulnerabilities, and the shifting landscape of risk and response. There’s a healthy dose of reality, some optimism about the tools and best practices available, and plenty of good advice, especially for smaller teams and freelancers who may not have access to enterprise-level resources.
If you care about keeping your WordPress sites secure, or want to understand where the community’s biggest concerns and opportunities are in 2026, this episode is for you.
Useful links
WordPress Security Statistics 2026: Melapress Survey Results
Matt: RIP Eric Binnion
For the next 30 days, a few billion of you will get an extra header in honor of Eric Binnion. The code in Nginx to do this is poetic:
add_header X-Remembering "Eric Binnion <https://friendsofericbinnion.wordpress.com/>" always;
Our design team will make that less AI and more humane in the coming days.
Automattic.com will have a mourning band for 30 days.

Eric was the 21st recipient of the Distinguished Janitor Award, Automattic’s highest honor, and in our hangs the last few months we’ve been talking about how to redefine and evolve it, which will happen internally at Automattic. One of the ideas was for the award to come with a physical memento, an etched tungsten cube. I don’t have many words so I’ll share something I wrote to Eric a few months ago when I gave him my cube when he was going through chemo.
Two Totems To Take With You
The first is a tungsten cube I keep on my desk. Its weight will surprise you, but tungsten is singular in having the highest melting point of any metal. That represents one of the things I admire most about you.
Tungsten has an atomic number of 74, its symbol is W, and it’s also known as wolfram.
My next post I’ve had in drafts for a while so please try to imagine me happy and promotional when reading it, but otherwise, I’m wrecked. Just going to soldier through because that’s what Eric always did.

OpenStation Blog: I Deleted 168,000 Lines of Comments. My AI Agent Didn’t Notice
Almost a third of our source code was comments. I deleted all of them and asked an AI agent to build the same features on both versions of the codebase, three times each. The code it wrote was just as good with or without comments.
If you use agents on a real codebase and wonder whether comments help them, slow them down, or don’t matter, here’s what I found.
Why I tried this
In this video (around 23:07), Lauren mentions that they don’t let their agents write comments in the code. Our codebase, is the opposite: it’s full of comments, and most of them were written by agents.
So I wondered: are all those comments helping the agent, or are they just extra text it has to read?
The experiment in one paragraph
I made a copy of the codebase with every comment removed, about 168,000 lines in total. Then I gave the same task to the same agent on both copies, three times on each, and checked the results the same way. I did this for two tasks, a small one and a bigger one.
The results
Every run passed every check: lint, type checks and the existing tests, plus, on the bigger task, a hidden test the agent never saw. A separate AI judge scored each result without knowing which copy it came from (more on that below).
Small task: tile all open windows (score out of 19)
| Branch | Score | Tokens | Cost |
|---|---|---|---|
| With comments | 18.3 | 2.18M | $1.42 |
| Without | 19.0 | 1.71M | $1.04 |
Bigger task: keep a window on top (score out of 23)
| Branch | Score | Tokens | Cost |
|---|---|---|---|
| With comments | 21.7 | 9.06M | $3.84 |
| Without | 22.0 | 9.12M | $3.95 |
The numbers are averages of three runs. The score differences are within noise, and so is the cost on the bigger task. On the small task, the agent used about 22% fewer tokens without comments, which makes sense: there was simply less to read.
The bigger task had a trap. The pinned state has to survive a page reload, and the PHP function that saves the window session drops any key it doesn’t know. Miss it and the feature looks fine until you reload. That’s exactly the kind of thing you’d expect a comment to help with. All six runs found it, with and without comments.
Why one run is not enough
My first plan was to run each branch once. I’m glad I didn’t.
On the bigger task, the three runs with comments used 8.21M, 8.79M and 10.17M tokens. The three runs without comments used 7.01M, 9.70M and 10.64M.
If I had picked one run from each branch, I could have written two opposite blog posts. Comparing 10.64M with 8.21M, removing comments makes the agent 30% more expensive. Comparing 7.01M with 10.17M, it makes the agent 31% cheaper. Same task, same code, same day.
Agents are not deterministic. If you’re measuring one, run it more than once.
How I ran it
- The agent: Claude Code with Opus 5.5 at high effort. Same model and settings for every run.
- The two codebases: our main branch, and a copy with the comments removed. I compiled both and checked that the resulting code is identical. The only comments left are the ones the tools need to work, such as lint directives and plugin headers, about 800 lines.
- The tasks: two real features, with the same prompt on both branches.
- The checks: the project’s own lint, type checks and tests. On the bigger task, also a hidden test I added after the agent finished, so it couldn’t write code just to pass it.
- The judge: a separate Claude session read each change and scored it against a checklist written before the runs: does it work, does it follow the project’s conventions, does it have tests, and so on. The changes were labelled with random names, so the judge didn’t know which branch each one came from.
- The runs: three per branch per task, alternating branches so that time of day affected both equally.
My conclusion
For the agent, code comments don’t make a difference to the quality of the code it writes. They don’t help, and they don’t hurt.
So keep a comment or delete it based on what it does for the people reading the code, not for the agent.
This doesn’t prove comments have zero effect. I tested one model, two tasks and three runs per branch, which is enough to rule out a big effect, not a small one.
Next: comments made no difference, but removing our docs/ folder and AGENTS.md did. That’s the next post.
Appendix: data and links
- The codebase with comments
- The codebase without comments
- Exactly what was removed (GitHub may only show part of it)
- Two of the small-task runs as pull requests: with comments, PR 974 and without comments, PR 975
- Full results, all runs: results page
- If you want to see the experiment script and the rubrics, they are all here
- Lines of code, measured with
scc:
| With | Without | |
|---|---|---|
| Whole repository | 765,491 | 597,332 |
| Plugin source code | 408,527 | 280,421 |
Matt: Neal Stephenson Live!
Speaking of sci-fi authors, Automattic is hosting Neal Stephenson for a livestream about his new book soon, please tune in!
Neal was a big influence on WordPress! I got hip to him from Tantek. In the source code of billions of pages you’ll see this:
<link rel="profile" href="https://gmpg.org/xfn/11">GMPG is the Global Media Protocols Group, “an experiment in Metamemetics.” Inspired, of course, by the Global Multimedia Protocol Group that owned the virtual real estate in Snow Crash’s metaverse.
Eric, Tantek, and I were reacting to the idea that there should be a separate heavily-marked-up RDF or XML web, and that HTML couldn’t be extended or enriched with metadata in a way that was beautiful to both humans and machines. It was really an aesthetic war. (It later got more built out in Microformats.)
We should revisit some of those principles because the web could use more distribution right now.
Open Channels FM: Balancing AI Efficiency Costs and Value in Markdown Data and Open Source Security
In today’s news, markdown streamlines AI input, AI-generated security reports increase workloads, and autonomous agent costs affect project efficiency
Course Platform Fees Compared: 14 Platforms to Sell a Course (+ Free Calculator)
We compared fees on Teachable, Kajabi, Stan, Udemy, WordPress LMS plugins, and more. Plug your own numbers into our free calculator to see the real cost!
The post Course Platform Fees Compared: 14 Platforms to Sell a Course (+ Free Calculator) appeared first on Themeisle Blog.
Open Channels FM: Open Channels FM Heading to the Web Summit 2026 in Lisboa
Next month in November, I’ll (Bob) be attending the Web Summit in Lisbon, Portugal. I have been to conferences in the past that have had attendance up to 15,000, but never one that has over 70,000 attendees. That’s a lot of people. A few months ago I applied for media creditation, unsure of their parameters […]
OpenStation Blog: What WordPress would have looked like in 1995
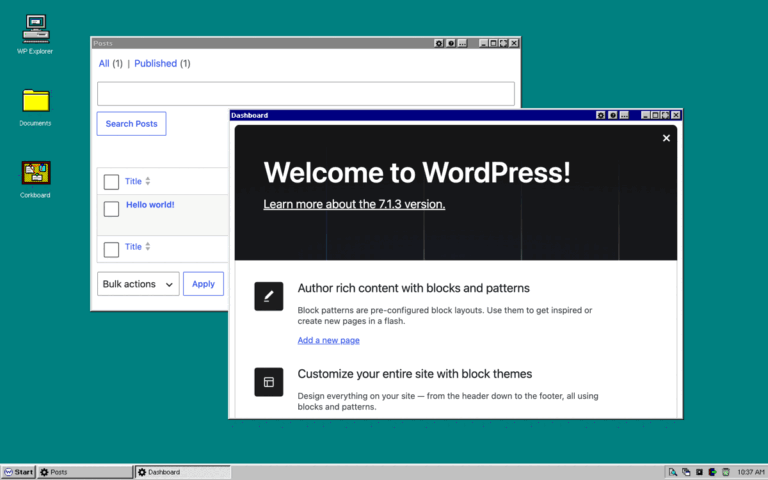
I’ve been wondering how far a theme can take OpenStation. Not just a wallpaper and a different color, but everything: windows, dock, menus, fonts, icons, layouts, etc. So I tried to make wp-admin look like two operating systems from a long time ago.

Retro 95 reimagines wp-admin as Windows 95. It even comes with a Start menu! And the classic clock sitting in the bottom-right corner is also there. You can try it live.

Retro 84 is the counterpart for Apple fans. It turns wp-admin into the first graphical OS that many people ever saw: the original Macintosh’s System 1. The beloved monochrome display, the classic pixelated font, and more! Check out the live demo.

And here’s a fun fact: every icon is pixel art typed into a text file, one character per pixel. The fonts were also made the same way, letter by letter.

Underneath, it’s the same wp-admin as always, just a few decades older.
If you want to build your own theme, the docs list everything a theme can change. Maybe it’s time for a proper Windows Vista comeback.
WordPress MCP Adapter Explained: What It Is, What It Exposes, and Your Options
The WordPress MCP Adapter is now a WordPress.org plugin. See what it exposes on your site, who can use it, how to keep it narrow, and your options.
The post WordPress MCP Adapter Explained: What It Is, What It Exposes, and Your Options appeared first on Themeisle Blog.